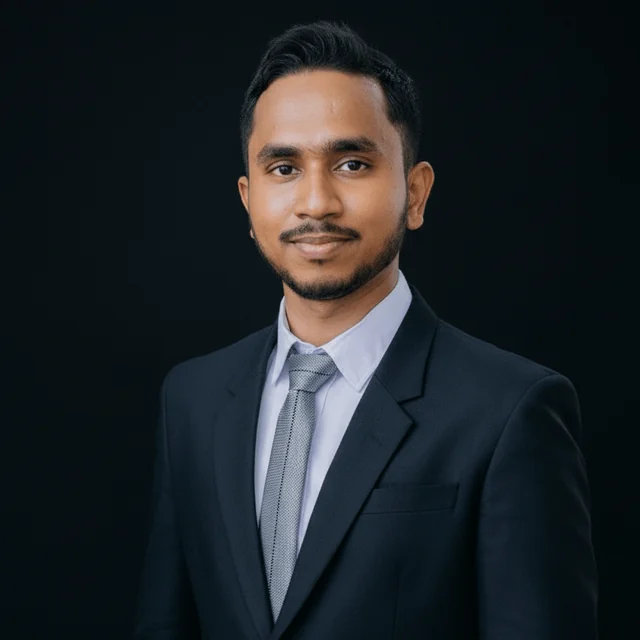
01 About
I'm a backend engineer in Colombo. Most of my work is designing APIs and integrations for internal services and automating workflows, often with web scraping and scripting. I like getting hands-on with what runs underneath: Linux servers, deployments, cloud infrastructure on Azure and Oracle, and IoT devices and microcontrollers.
Security is a constant interest. I review systems for weaknesses and have a basic hands-on background in penetration testing. I also write about how the internet's cryptography works at randhana.com.
PHP · Python · Node.js · FastAPI · SQL Server · MySQL · Redis · Docker · Linux · CI/CD
BSc in Physical Science & ICT, University of Sri Jayewardenepura (2023)
02 Featured work
-
Fixed-deposit rate comparison
Tracks fixed-deposit rates across banks and finance companies in Sri Lanka. Scraping pipeline, FastAPI API, Next.js frontend.
Live
-
JWT decoder
Paste a token to read its header and claims. It runs in your browser, and nothing is sent anywhere.
Tool
-
Drowning Detection System
Final-year university project, 2023. Detects drowning in recorded video with computer vision and pre-trained models. 47 stars on GitHub.
Open source
03 Writing
-
How HTTPS really works
TLS handshakes, certificates, and encryption, explained from the network up.
-
Why the lock icon lies on a company laptop
What the padlock does and does not guarantee on a managed computer.
-
Production-grade secure authentication API
Design decisions behind a JWT auth API with refresh token rotation and role-based access control.
04 Handshake
Every HTTPS connection starts with a handshake. Here is what each message reveals, and what it hides from someone watching the network.
What someone watching the network can see.
- ClientHello. The client sends a random value, the TLS versions it supports, and its own X25519 key share.
- ServerHello. The server picks a cipher and returns its key share. Both sides can now compute the same shared secret. This message is not encrypted.
- Encrypted flight. The server sends its certificate and a signature over the handshake, encrypted with keys derived from the shared secret.
- Verification. The client checks the certificate chain and hostname against trusted roots, then verifies the signature with the certificate's key.
- Client Finished. The client proves it derived the same keys. The handshake is complete after one round trip.
- Application data. Data flows under the derived traffic keys. Nothing on the wire is readable without them.
05 Now
Building a rate limiter in Go and studying for AZ-104.
Updated
06 Links
- GitHubgithub.com/randhana
- Blograndhana.com
- LinkedInlinkedin.com/in/pulathisi-kariyawasam
- Xx.com/RandhanaK
- Emailpulathisi.kariyawasam@gmail.com
-
PGP
Public key (.asc)
BE01 4195 B028 9652 2D79 876B 9444 1258 17B4 0699